Fractional vCISO · Security & AI governance

Security,
sized right.

Senior security leadership for startups and growing companies — without a full-time CISO. Security governance, SOC 2 readiness and the AI tools your team already uses, managed as one program and scoped to where you are now.

The pin-high principle
Too short
Gaps that customers, auditors and attackers find first.
Pin high
The right controls for your stage — nothing missing, nothing wasted.
Too long
Enterprise-grade process and tooling you don’t need yet.
Built for
  • Early-stage SaaS startups
  • PE & VC portfolio companies
  • Teams facing a first SOC 2
  • Companies adopting AI fast

Three ways to work together.

Most clients start with one and grow into another. Every engagement is scoped to your size, budget and deadline — not a template.

01 · Ongoing

Fractional vCISO

Security leadership a few days a month — for when questionnaires, board questions or investor diligence start landing and nobody owns security.

  • Security program roadmap & policies
  • Risk register and prioritization
  • Customer questionnaires & vendor reviews
  • Incident response & continuity planning
  • Board and investor reporting
Monthly retainer
02 · Project

SOC 2 Readiness

From gap assessment to audit-ready, with controls that make business sense for a company your size — not a 200-page binder.

  • Gap assessment against the Trust Services Criteria
  • Right-sized control set and policy pack
  • Evidence collection and tooling guidance
  • Auditor selection and audit support
Fixed-scope project
03 · Specialty
Security + AI

AI Security & Governance

Let your team use AI tools and agents without creating a new class of risk — guidance from a practitioner who governs AI in production, not just on paper.

  • AI use inventory and acceptable-use policy
  • Vendor and model risk reviews
  • Approval process for agents, connectors & MCP
  • Alignment with NIST AI RMF and ISO 42001
Assessment + program
Also available as standalone projects
  • Risk assessment
  • Vulnerability management program
  • Incident response & business continuity
  • Security awareness & culture
  • IT strategy & tech-stack advisory
  • IT asset management & planning
Where security meets AI

AI didn’t replace security. It raised the stakes.

New tools, new data flows, new vendors and new ways for things to go wrong. I’m a security leader first, and I bring AI into your program the same way I’d bring in any other system: deliberately, with the controls it actually needs.

SECURITYAI

Security first

Every AI control rests on the fundamentals: identity, data handling, vendor risk and incident response. Get those right and AI governance has something to stand on.

AI in scope

Copilots, agents, connectors and models get the same rigor as any other system: an inventory, an approval path, monitoring and an owner.

One program

One roadmap, one risk register, one person accountable. AI risk lives inside your security program, not in a separate committee beside it.

How an engagement works.

Same shape whether it’s a SOC 2 project or an ongoing vCISO role. You always know what’s next and why.

  1. 01

    Assess

    A short, fixed-length discovery: interviews, a review of what you already have, and a clear read on your real risks and obligations.

  2. 02

    Right-size

    A prioritized roadmap: what to do now, what can wait, and what you can skip entirely. Every item tied to a business reason.

  3. 03

    Run it with you

    Hands-on execution alongside your team, with reporting your board, customers and auditors can actually use.

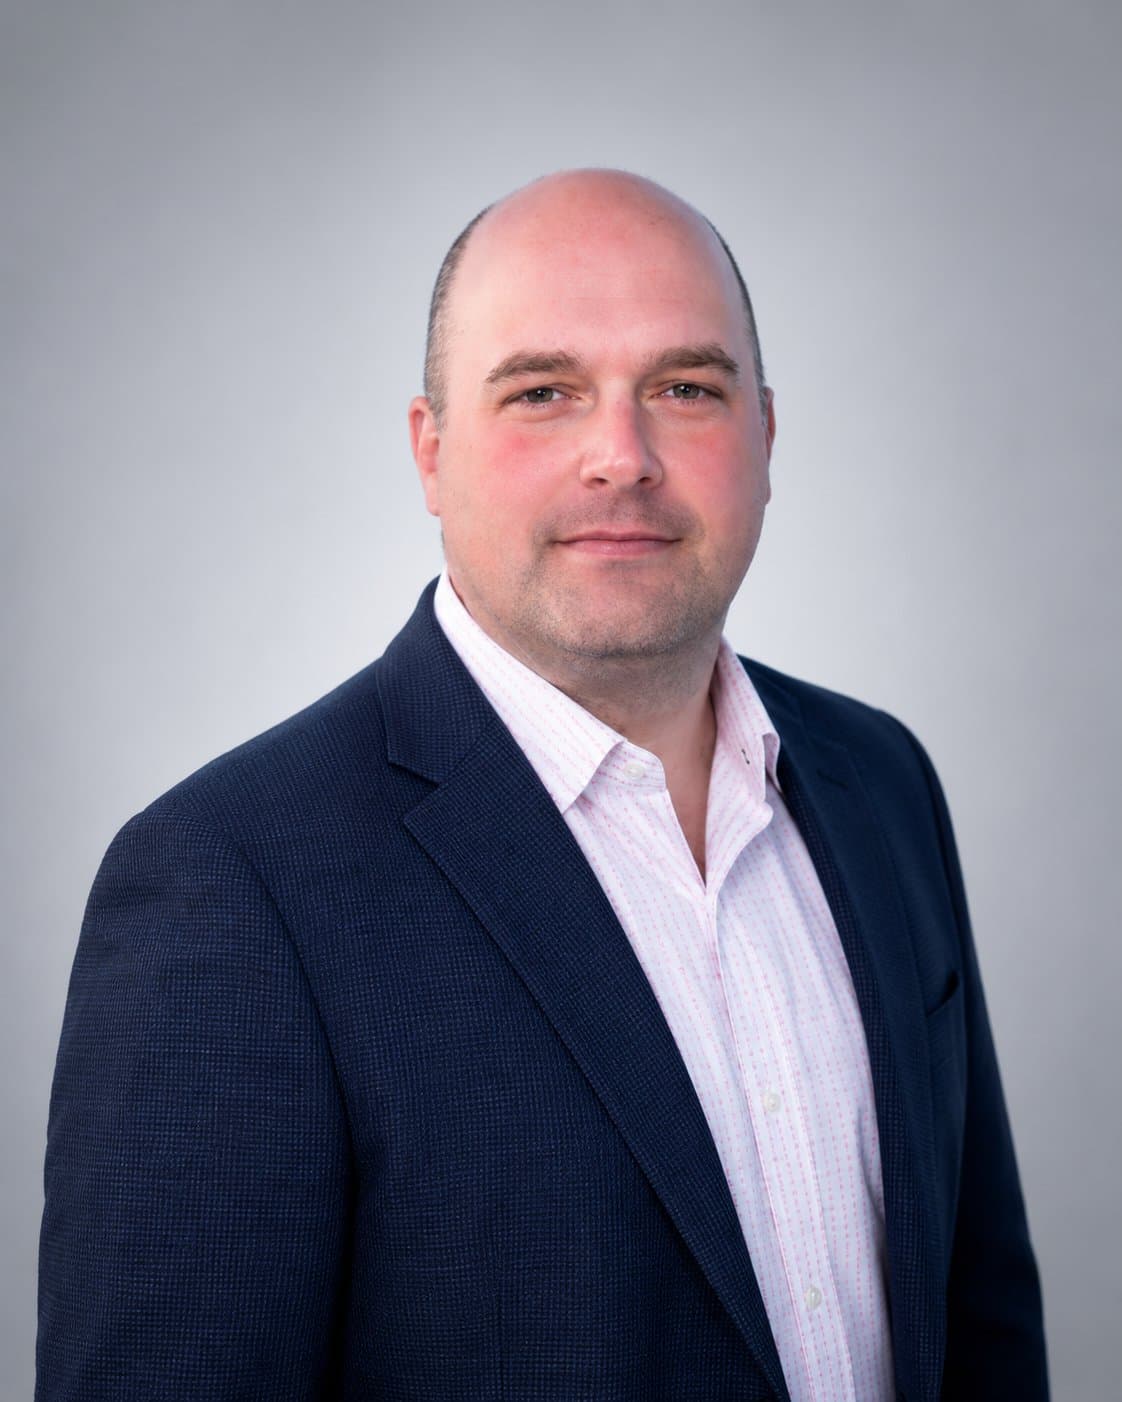
Matt Huber, Founder and Principal of PinHigh Advisory
Who you’ll work with

Matt Huber

Founder & Principal. 20+ years in technology, with deep experience in security governance, compliance and AI risk. Matt co-founded Aware, a collaboration security company, and took it from startup to acquisition in 2024 — so he builds security programs the way founders need them: in step with the business, never in its way.

You work with Matt directly. No hand-off to junior staff after the sales call.

20+
years in technology
Founder
security startup founder, one exit
CISSP
certified
Why “PinHigh”?

In golf, a shot that finishes pin high has the distance exactly right — not short, not long. That’s the job here: security, IT and AI programs sized correctly for where you are today, with room to grow.

Questions.

Why not just hire a full-time CISO?

Until security is a full-time job at your company, a fractional leader gives you the same strategic judgment at a fraction of the cost — and scales up or down as you grow.

How is this different from a large consulting firm?

No cookie-cutter frameworks and no over-engineering. You get practical governance and controls that fit your actual needs and budget, from someone who understands how startups and SMBs operate.

Can you get us SOC 2 ready?

Yes. From the initial gap assessment through audit readiness, with cost-effective controls that make business sense.

What if we don’t need a full program?

That’s common. Choosing a tech stack, standing up asset management, or just a second opinion on best practices — flexible, project-based support works too.

Find out where you stand.

A 30-minute call. You’ll leave with a clear read on your biggest gaps — whether or not we work together.